About Strand

Built by investigators, for investigators

Strand Intelligence is a UK-based automated digital forensics and incident response platform that investigates security incidents for IR firms, critical national infrastructure, regulated enterprises and government.

EDR tells you something happened. Strand tells you how it happened, what was affected and whether the attacker is still there, with the evidence for each finding.

What Strand does

Evidence collection

Collect evidence from endpoints, servers and cloud tenants, including Microsoft 365, Entra ID, Azure and Google Workspace. Existing KAPE and Velociraptor collections, plus EDR and SIEM telemetry, can join the same investigation.

Incident investigation

Reconstruct initial access, lateral movement, persistence, data impact and root cause. Strand brings the evidence together into a single timeline and links findings to their sources with a confidence level.

Forensic reporting

Generate reports for executive, technical, legal and client audiences. Analysts retain judgement and final conclusions, and IR firms can deliver reports under their own brand.

Continuous compromise assessment

Run daily forensic threat hunts across the cloud estate, including when no alert has fired. Each hunt produces a dated, evidence-backed record aligned to the NCSC Cyber Assessment Framework.

Explore the platform modules

What makes Strand different

Collection that can start mid-incident

Strand’s collectors can be deployed during a response, so an investigation does not depend on the client’s existing telemetry. Teams can also bring collections they already hold.

Findings backed by evidence

Every finding links to supporting evidence and a confidence level. Analysts retain the judgement and final conclusions while Strand automates the investigation work.

A platform for response firms

Strand supports the firm’s analysts rather than competing as an IR service. White-labelled reports and per-investigation pricing support incident-driven work.

Independent assurance between incidents

Daily compromise assessments look for what the SOC or MDR may have missed. Evidence supports assurance and reporting; accountability for compliance remains with the organisation.

Who uses Strand

  • Incident response firms and DFIR consultancies handling ransomware, business email compromise and other security incidents.
  • Critical national infrastructure operators in telecoms, water and energy seeking continuous compromise assessment.
  • Regulated enterprises, including financial services organisations, requiring defensible investigation and assurance records.
  • Government and public sector teams investigating incidents and gathering evidence for assurance programmes such as GovAssure.

Find Strand for your team

How Strand works

  1. 01

    Collect the evidence

    Deploy Strand’s collectors or ingest existing collections and security telemetry from the affected environment.

  2. 02

    Reconstruct the incident

    Strand correlates the evidence, builds the timeline and investigates root cause, persistence and data impact.

  3. 03

    Deliver the findings

    Analysts retain final judgement, with evidence-linked findings and reports for the people who need answers.

The team behind Strand

Strand was built for responders who need defensible answers fast. The founders combine hands-on DFIR experience, regulatory investigation background and enterprise software delivery.

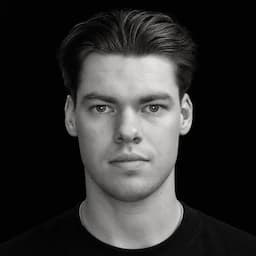
William Jude-Poole

Co-Founder

Chief Executive Officer

William Jude-Poole

Regulatory investigations at the ICO, then Technical Director at a UK DFIR firm. I've seen incidents from every angle. The constant was good people stretched too thin, doing important work with inadequate tools. We built Strand for them, and for the organisations counting on them.
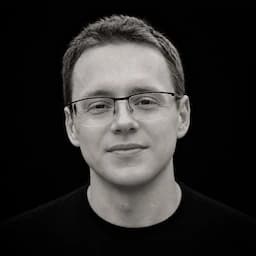
Oli Fletcher

Co-Founder

Chief Operating Officer

Oli Fletcher

Years spent leading large teams to deliver AI-driven innovation into complex enterprises, turning ideas into commercial outcomes. I focus on building solutions that integrate seamlessly into operations: powerful enough to change performance, simple enough to deploy without friction.

Founding Team

Will Burton

Sales

Will Burton

Five years in B2B sales and business development across a wide range of markets. Now developing Strand's sales function into a globally scalable model.

Jordan Newman

Threat Research

Jordan Newman

Computer scientist with a background in intelligence, network security and systems exploitation. Tracks threat groups and their evolving techniques to keep Strand intelligence-driven.

Sean Dingsdale

Engineering

Sean Dingsdale

Engineering leader experienced in security platforms, AI-enabled products and scalable cloud infrastructure.

Follow Strand on LinkedIn (opens in a new tab)

Key facts

Company
Strand Intelligence
Offering
Agentic AI digital forensics and incident response automation platform
Founders
William (Will) Jude-Poole, CEO; Oli Fletcher, COO
Headquarters
Manchester, United Kingdom
Backing
Osney Capital
Certifications
ISO 27001 and Cyber Essentials Plus
Data processing
UK by default, with global data planes available
IR firm pricing model
Per investigation

Explore security and data handling in our Trust Center

Frequently asked questions

Does Strand replace our EDR, SIEM or MDR?

Strand complements these tools. It investigates the incidents and alerts they detect and runs forensic hunts for activity they may have missed.

Can Strand be deployed during an incident?

Yes. Strand’s collectors can be deployed mid-incident, and the platform can also ingest existing KAPE and Velociraptor collections alongside EDR and SIEM telemetry.

Who approves the investigation findings?

Analysts retain judgement and the final conclusions. Strand automates evidence collection, investigation and report generation, with each finding linked to supporting evidence and a confidence level.

Where is evidence processed?

Strand processes data in the UK by default, with global data planes available. Deployment and data-residency requirements can be discussed with the team when arranging a demo.

How is Strand priced for incident response firms?

Pricing is per investigation to suit incident-driven work. Contact the team to discuss your investigation requirements and obtain a quote.

See Strand in your investigation workflow

Discuss your incident types, evidence sources and deployment requirements with the team.